
SECURITY & DATA PROTECTION AT BOOK CLARITY
Your Financial Data
Deserves Serious Protection
When you work with Book Clarity, your financial data is shielded by enterprise-grade security protocols, rigorous access controls, and separated environments. We treat your bank statements, tax documents, and payroll records with the absolute highest level of protection.
SECURITY ARCHITECTURE STACK
How Book Clarity Protects
Your Information
Secure
Accounts
Multi-Factor
Authentication
Environment
Separation
Device & OS
Standards
Infrastructure
Safeguards
Storage & Access
Policy
Fraud & Credential
Protection
Security Procedures
& Incident Response
* Team Members refers to our internal staff, contractors, and authorized partners who are granted specific, scoped access to systems strictly necessary for their role.
IDENTITY MANAGEMENT
Authentication &
Access Control
Multi-Factor Authentication
Passwords alone aren't enough. Our robust authentication framework ensures that compromised credentials cannot be used to access sensitive financial data. We require multiple independent layers of verification before granting system access.
- Time-based one-time passwords (TOTP)
- Hardware security key integration
- Biometric verification on managed devices
Individual User Accounts
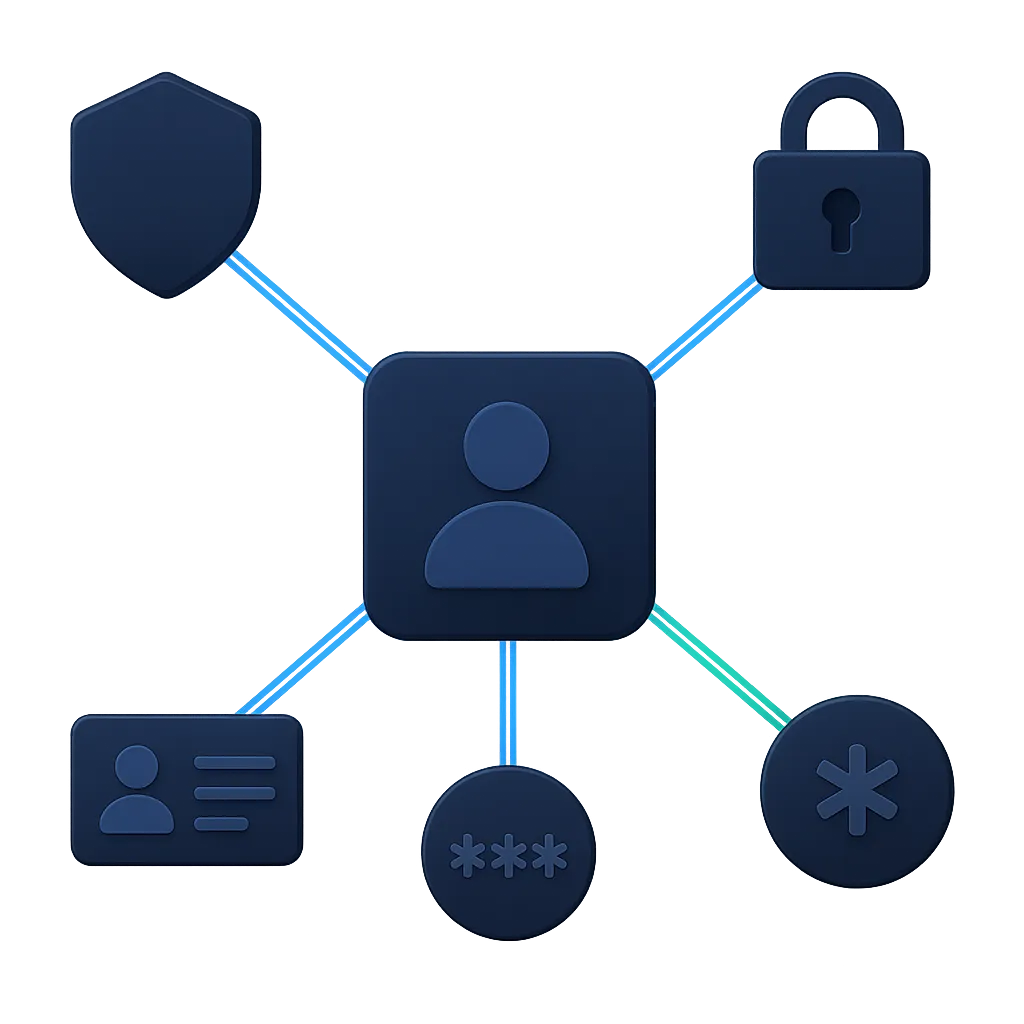
Every user operates within a rigidly defined permissions boundary. Our Identity Management system ensures the flow from Team Member to Assigned Permissions is strictly monitored and enforced, creating an immutable audit trail for every action taken within the environment.
Data Isolation
Dedicated Book Clarity
Work Environments
To ensure complete data isolation, our team members operate within strictly controlled, dedicated work environments. A single physical device is strictly partitioned at the operating system level, creating an impenetrable boundary between personal use and Book Clarity operations.
Inside the secure Book Clarity work boundary, only authorized applications are permitted to run. This zero-trust approach ensures your financial data is never exposed to unvetted software or personal applications.
- Double
- QuickBooks Online (QBO)
- Google Workspace
HARDWARE STANDARDS
Protected Employee &
Contractor Computers
Strict operating system and security configurations are mandatory for all devices accessing company data.
Windows Systems
Operating System: Windows 10 Pro or Windows 11 Pro required.
Data Encryption: BitLocker Drive Encryption enabled and configured.
Endpoint Security: Windows Defender Antivirus active with cloud protection.
Network Defense: Built-in Windows Firewall enabled for all network profiles.
macOS Systems
Operating System: macOS 12 Monterey or newer required.
Data Encryption: FileVault 2 Disk Encryption enabled.
Endpoint Security: XProtect and Gatekeeper active.
Network Defense: Built-in Application Firewall enabled.
Device Encryption
All contractor and employee devices must have full-disk encryption enabled (BitLocker for Windows, FileVault for macOS) to ensure data at rest remains secure in the event of hardware loss or theft.
Secure Network &
Workspace Environment
Secure Network Access
All remote team members are strictly required to connect via a trusted, encrypted network framework. Accessing company systems over public or unsecured Wi-Fi is actively monitored, flagged, and blocked to ensure client data is never exposed in vulnerable environments.
Secure Google Workspace Environment
Our entire operational infrastructure is housed within a hardened Google Workspace environment. We implement comprehensive administrative policies that control precisely how data is accessed, stored, and shared.
- Enterprise-grade Mobile Device Management (MDM) ensures all devices meet strict security baselines before access is granted.
- Mandatory Hardware Security Keys (FIDO2) are enforced for all administrative and high-level financial access layers.
- Comprehensive Data Loss Prevention (DLP) protocols actively prevent unauthorized external sharing of sensitive records.
- Real-time threat detection and automated anomaly response are persistently active across all Workspace applications.
- Granular Organizational Units (OUs) compartmentalize data, restricting access strictly to personnel with verified clearance.
LEAST-PRIVILEGE APPROACH
Controlled Storage &
Limited Downloads
We enforce a strict separation between managed environments and local storage. All work occurs within authorized boundaries to ensure financial data never resides where it cannot be actively secured and monitored.
Controlled Storage
Data is housed exclusively within our authorized, highly monitored cloud environments with strictly enforced zero local retention policies.
Personal Storage Is Not Approved
Under no circumstances is client information permitted to be saved to personal devices, USBs, or unmanaged local drives.
Controlled Access
Team members are granted access strictly on a least-privilege basis, exposing only the precise data required for their active tasks.
Approved Technology &
Service Providers
QuickBooks Online & Approved Technology
Double states that its platform strictly limits third-party access. All approved technology and service providers, including QuickBooks Online (QBO), are vetted for compliance with industry-standard data protection protocols. Double states that integration points employ least-privilege access, ensuring your financial data remains isolated and secure.
Double Security Certifications
- Double states it maintains SOC 2 Type II certification, verified by independent third-party auditors.
- Double states that all sensitive data is protected using AES-256 encryption at rest and TLS 1.2+ in transit.
- Double states that continuous infrastructure monitoring detects and mitigates threats in real-time.

How Double Handles AI
Double states that its artificial intelligence models do not use your proprietary financial data for public training. Data flows through secure, isolated pipelines where model provider relationships are strictly governed by enterprise-grade non-disclosure agreements.
Responsible Use of AI
Double states that AI tools are deployed solely to enhance processing efficiency and accuracy. Human oversight remains mandatory for all critical financial categorizations and reporting functions.
Security Designed for
Remote Work
While our infrastructure provides deep technical safeguards, the human element of remote work remains a critical vulnerability. Our comprehensive remote work policies ensure that our team maintains enterprise-grade security standards, regardless of their physical location.
Screen Privacy Locks
All devices are equipped with physical privacy screens to prevent shoulder surfing in semi-public spaces.
Encrypted Wi-Fi
Connections to WPA3 encrypted networks are mandatory. Open or public Wi-Fi is strictly and technically prohibited.
Physical Security
Strict zero-paper policy. No sensitive client data may ever be printed or stored physically in remote environments.
Mandatory VPN
All remote traffic is strictly routed through our enterprise VPN with military-grade IPSec encryption.
Session Timeouts
Devices automatically lock after exactly 5 minutes of inactivity, requiring biometric re-authentication to resume.
Secure Networks
Employees must adhere to strict guidelines for securing their home network routers and segregating IoT devices.
Unattended Locking
A strict zero-tolerance 'lock on walk away' protocol is enforced, even within private home environments.
Clear Desk Policy
Remote workspaces must remain free of any visible sensitive information at all times, verified by random checks.
These policies are strictly enforced through automated compliance checks and regular security training, ensuring that client data is never exposed in remote environments.
SECURITY STANDARDS
Phishing & Credential
Protection
Phishing & Financial Fraud Awareness
We maintain strict verification protocols for all financial movements. Treat the following high-risk requests as immediate red flags, as they bypass our standard authenticated communication channels.
- Urgent or unexpected requests for ACH or wire transfers.
- Instructions to change payment details via email.
- Requests for sensitive credentials outside our secure portal.
Password & Credential Protection
Your access credentials are the first line of defense. We enforce rigorous identity and password policies to ensure your business data remains strictly isolated and impenetrable.
- Mandatory multi-factor authentication (MFA) on all accounts.
- Complex, unique passwords rotated every 90 days.
- No credential sharing across personal and work environments.
Data Retention &
Incident Response
Data Retention & Secure Disposal
Client financial data is retained exclusively for the duration of the active engagement or as mandated by financial regulations. Upon conclusion, all records undergo cryptographic wiping protocols, ensuring secure and irrecoverable disposal across our entire infrastructure.
Security Incident Response
Our dedicated security operations center operates continuously to detect, isolate, and remediate potential threats before they impact your financial data. The 5-stage framework ensures swift, systematic resolution with complete architectural transparency.
Offboarding
Complete access revocation is executed simultaneously across all platforms. Work environments are decommissioned, devices are systematically wiped remotely, and final security audits are provided to guarantee zero residual access.
Ongoing Security Reviews
We conduct persistent compliance monitoring and quarterly penetration testing. Security protocols are continuously updated to outpace emerging threats, ensuring your financial ecosystem remains impenetrable over the long term.
ARCHITECTURE SUMMARY
Our Security Philosophy
Protect the Device. Protect the Account. Limit the Access. Protect the Data.
Protect the Device
Enforcing strict OS standards, MDM policies, and hardware-level isolation to ensure endpoints remain uncompromised.
Protect the Account
Deploying mandatory MFA, biometric verification, and session timeouts to eliminate credential-based threats.
Limit the Access
Applying zero-trust network principles and role-based permissions so users only reach what their task requires.
Protect the Data
Implementing end-to-end encryption at rest and in transit, alongside DLP safeguards to prevent exfiltration.
Your Trust Matters
At Book Clarity, we recognize that you entrust us with your most sensitive financial data. This responsibility is the foundation of our business. We are unconditionally committed to maintaining the highest standards of security, privacy, and compliance to ensure your information remains protected at all times.
Our approach is proactive, transparent, and continuously evolving to meet the challenges of a dynamic digital landscape. We view security not just as a technical requirement, but as a fundamental promise to our clients.
Important Information About This Security Overview
The security measures, protocols, and architectural standards described in this page represent our current practices as of the date of publication. Because the cyber threat landscape is constantly evolving, our practices are subject to continuous review and may be updated, enhanced, or modified as part of our ongoing commitment to robust data protection. This overview is provided for informational purposes only and does not constitute a legally binding agreement, warranty, or guarantee of absolute security.
Book Clarity Values
RELIABILITY
SERVICE
EXCELLENCE
TRUST

RELIABILITY
Consistent, dependable support you can count on every time.

SERVICE
Dedicated assistance focused on meeting your needs with care.

EXCELLENCE
High-quality results with professionalism and precision.

TRUST
Building relationships through honesty, transparency, and integrity.

FOLLOW US


COMPANY
CONTACT US
LEGAL
Copyright 2026. Book Clarity LLC. All Rights Reserved.